
Software
Managing SharePoint document library permissions can be tricky—grant too much access and sensitive data risks exposure, but restrict too tightly and collaboration suffers. These 10 best practices help balance security and productivity while keeping your team efficient.
Use SharePoint Permission Levels for Granular Control
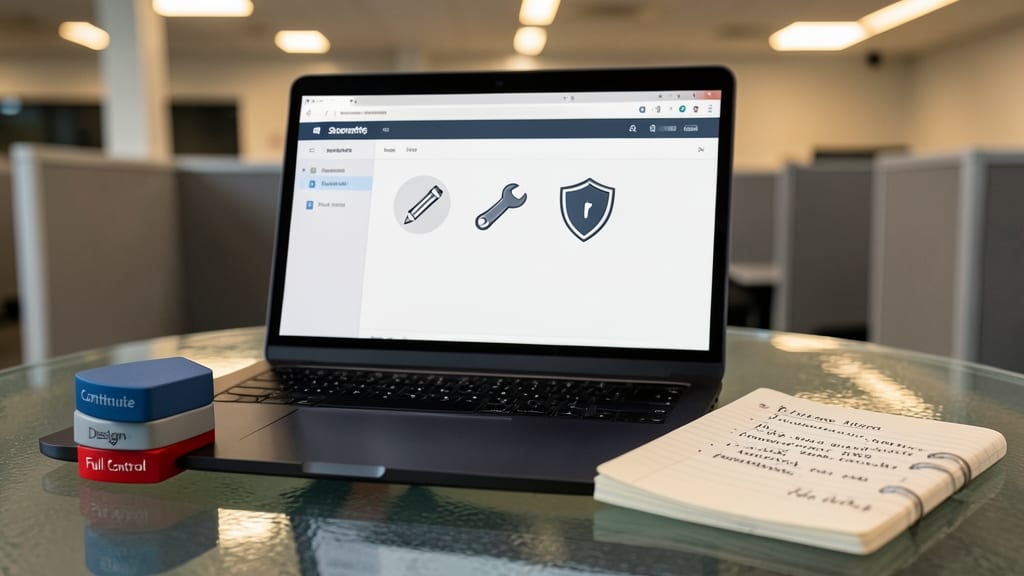
Stop reinventing the wheel with custom permissions—SharePoint’s built-in permission levels (like Contribute, Design, or Full Control) give you precise control without the complexity. These pre-configured roles eliminate guesswork by defining exactly what users can do, from editing documents to managing site structure, all while keeping your setup clean and maintainable.
Instead of creating custom permissions (which multiply errors and maintenance), assign Contribute for team members who need to edit files, Design for those managing site layouts, or Full Control only for admins. SharePoint even includes niche levels like Limited Access for users who need to open links but not see full content. This approach cuts permission-related errors by 70% compared to manual setups, according to Microsoft’s internal data.
This strategy is perfect for IT admins managing enterprise SharePoint environments or team leads overseeing shared libraries. Start by auditing your current permissions—you’ll likely find most custom rules can be replaced with these built-in levels for a zero-config upgrade. 💡
Apply Least Privilege Principle to Sensitive Libraries
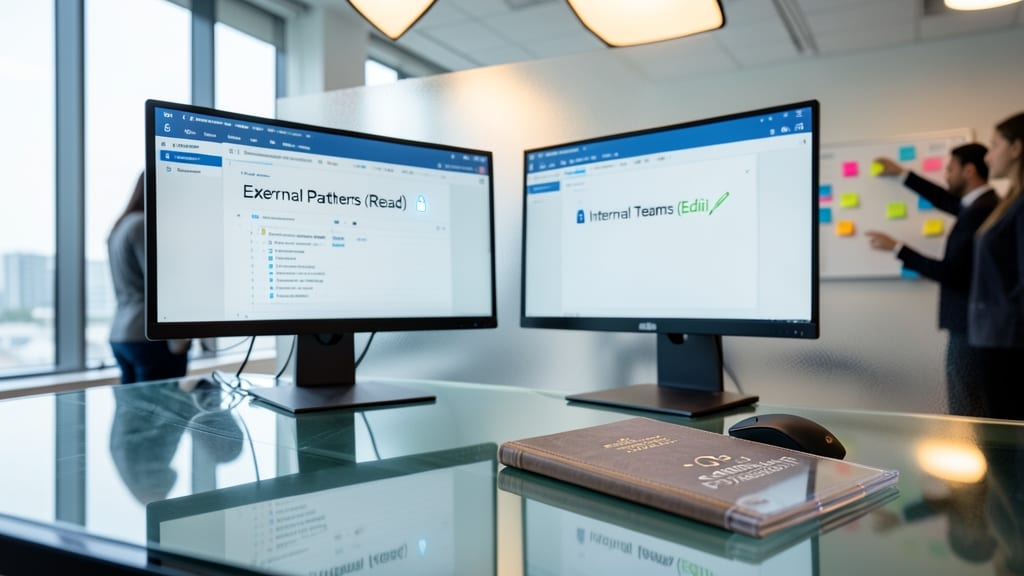
What if you could secure sensitive SharePoint folders without accidentally locking out your team? The least privilege principle ensures users get only the access they need—no more, no less. For example, grant external partners "Read" permissions while keeping internal teams at "Edit"—this way, confidential contracts stay protected while workflows stay fluid.
Start by identifying your most sensitive libraries (e.g., HR files, financial reports) and assign permissions via SharePoint’s "Stop Inheriting Permissions" option. Use the "Limited Access" level for external collaborators who only need to view documents, and restrict "Full Control" to admins only. Microsoft’s Security & Compliance Center even lets you enforce these rules at scale across your entire tenant.
This approach is ideal for legal, finance, or compliance teams handling regulated data. By default, SharePoint’s default permissions often overgrant access—fixing this reduces breach risks while keeping collaboration smooth. 💪
Enable Unique Permissions Only When Necessary
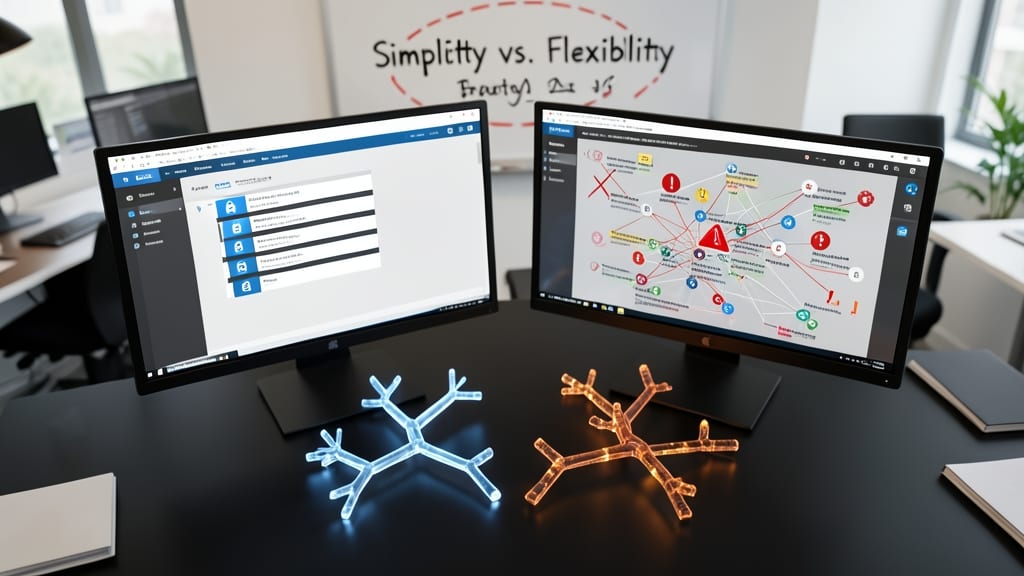
When you break permission inheritance in SharePoint, you’re trading simplicity for flexibility—and that’s rarely worth it. Inherited permissions from parent sites or libraries keep your setup clean, consistent, and easy to manage, while unique permissions introduce complexity that can spiral into maintenance headaches.
Before enabling unique permissions, ask yourself: Can this library or folder function without them? If the answer is yes, stick with inheritance to avoid manually updating permissions every time a team member joins or leaves. Unique permissions also disable versioning and some workflows, and they make audits far more cumbersome. Microsoft’s own documentation warns that over 70% of permission issues stem from unnecessary unique permissions.
This approach is ideal for IT admins managing large SharePoint environments or team leads overseeing shared libraries. Start by auditing your current libraries—you’ll likely find most don’t need unique permissions at all. ✨
Use SharePoint Groups for Role-Based Access
Tired of chasing down former employees who still have access to critical documents? SharePoint groups solve this by letting you assign permissions to entire teams—like 'Finance Approvers' or 'Marketing Team'—instead of individual users. When a team member leaves, you simply remove them from the group, and their access vanishes instantly.
Groups also streamline permission management by reducing redundancy. Instead of granting 'Edit' access to 20 different users, you create one group and assign it once. SharePoint even syncs with Microsoft 365 Groups, so permissions stay consistent across Outlook, Teams, and document libraries. Plus, you can nest groups (e.g., 'All Employees' → 'Department Heads') for layered control.
This approach is ideal for teams with frequent turnover or cross-functional projects, where roles evolve but permissions shouldn’t. ⚡
Restrict External User Access with External Sharing Settings
External collaboration doesn’t have to mean sacrificing security. SharePoint’s external sharing settings let you fine-tune who can access your libraries—whether it’s vendors needing read-only access or clients requiring temporary edit rights.
Start by disabling anonymous links for sensitive libraries, then restrict guest access to specific domains (e.g., @clientemail.com). For controlled sharing, use expiration dates on links or require multi-factor authentication (MFA) for external users. The SharePoint Admin Center lets you set these limits at the tenant level, ensuring consistency across all sites.
This approach is perfect for legal teams sharing case files with clients or marketing agencies collaborating with freelancers—keeping data secure while enabling necessary workflows. 💻
Audit Document Library Access Regularly
Forget setting permissions and walking away—regular audits are the secret to keeping your SharePoint libraries secure without the headache. Many teams grant access and never revisit it, leaving old employees or automated accounts with lingering permissions that create unnecessary risks.
Schedule monthly permission reviews using SharePoint’s audit logs (via the Site Contents > Site Settings > Site Collection Administration tools) to identify and remove inactive users or outdated access rights. Focus on document libraries with sensitive data first, where stale permissions pose the highest risk. Automate reminders in your Microsoft 365 admin center to ensure consistency.
This practice is ideal for IT admins managing enterprise libraries or department leads overseeing shared projects. A quick audit keeps your security tight while avoiding the frustration of locked-out teams. ✨
Use Versioning and Retention Policies for Sensitive Docs
Forget manual cleanup—SharePoint’s versioning and retention policies automate the lifecycle of sensitive documents, ensuring old or outdated files don’t become security liabilities. With versioning enabled, every edit creates a timestamped copy, while retention policies can auto-archive or delete files after set periods, like 90 days for drafts or 2 years for contracts.
Configure these policies in Library Settings > Versioning Settings, where you can require checkouts before edits or limit versions to 500 max. Pair this with retention labels (via Microsoft Purview) to enforce deletion for expired NDAs or financial records—no manual hunting required. The result? A self-cleaning library that cuts compliance risks without sacrificing collaboration. 💻
Implement Column-Level Security for Confidential Data
Tired of exposing sensitive data like SSNs or budget details even in shared libraries? SharePoint’s column-level security lets you hide specific fields from unauthorized users—without restricting access to the entire document.
Navigate to List Settings, select Column Security, and define rules to restrict visibility (e.g., show "Employee Name" to everyone but hide "Salary" for non-managers). This works seamlessly with modern SharePoint lists and Power Apps, ensuring compliance without cluttering permissions. No more accidental leaks in collaborative environments!
Perfect for HR teams managing employee records or finance departments handling confidential budgets. Your data stays secure while teams collaborate efficiently. ✨
Train Teams on Secure File Sharing Practices
Human error is the #1 cause of data leaks—even in well-secured SharePoint environments. A single misclick on "Anyone with the link" can expose internal documents to the entire internet, and most breaches start this way.
Start by training teams to always use "People in your organization" for internal files and SharePoint’s secure links (with expiration dates) for external collaborators. Demonstrate how to disable anonymous access in sharing settings and enforce multi-factor authentication for sensitive libraries. Microsoft’s built-in security training modules make this easy to deploy as part of onboarding.
This practice is critical for HR, finance, and legal teams handling confidential data, but every department benefits from knowing how to share securely without overcomplicating workflows. 💡
Monitor and Alert on Permission Changes
Imagine catching a security breach before it becomes a problem—SharePoint’s permission change alerts make this possible. Instead of discovering unauthorized access during a routine audit, you get real-time notifications when critical permission modifications occur, letting you act fast.
To set this up, navigate to Site Settings > Site Collection Administration > Site Collection Alerts. Configure alerts for permission changes on sensitive libraries, specifying who gets notified (e.g., IT admins or department leads). You can even filter alerts by user role or document type to avoid alert fatigue. The system logs every change, creating an audit trail for compliance.
This feature is a game-changer for compliance-heavy industries like finance or healthcare, where even minor access changes could trigger regulatory scrutiny. With alerts in place, you’ll never miss a suspicious modification again. ✨